AI Governance
A method to see, prioritize and govern the use of AI in your organization, whatever technology you use.
- Building and running technology since 2008
- Microsoft Partner since 2010
- 200+ large organizations as clients
- ISO 27001 certified
- 60+ in-house professionals in Barcelona and Madrid
- Our own SaaS services and solutions
The starting point
Tokenmaxxing or AI-Factory
Two ways to bring AI to the whole organization. Both can include Copilot, Claude or Gemini: what changes is what they work on.
Model 1 · Tokenmaxxing
Each area builds its own agents independently
- Autonomy and quick results in each area
- Hard for IT to govern: security, training, standards
- Growing and hard-to-predict token costs
- Automations built on unstable foundations
Result: the same human processes, only slightly more productive
Model 2 · AI-Factory
IT industrializes automation
- Copilot and approved agents, via MCP on top of governed software
- Automation at an unprecedented scale
- Tokens invested in building, not in using
- Requires an AI-Driven team and a change in IT
Result: an end-to-end digitalized organization
Capabilities, not raw data
Via MCP, approved agents use business operations from the ERP, the CRM or the document repository
One connector, any AI
Built once, it works for Copilot, Claude or Gemini. An open standard, with no vendor dependency.
IT keeps control
Permissions, rules and auditing live in the software, not in each agent.
What we achieve
01
Visibility
IT knows which AI is used in the organization, corporate or not.
02
Less risk
Reduce shadow AI: sensitive data, compliance and legal exposure.
03
Productivity
Automate the highest-value opportunities from IT.
04
A clear path
Determine the organization's maturity and chart the path to governed AI.
05
IT as enabler
Let IT drive AI adoption, not hold it back.
An assessment through three perspectives
Objective data, the voice of users and an X-ray of the organization. Independent of the technologies you have.
Telemetry
Reality
Which AI is actually used, corporate or not, based on objective data. The map of real risk.
- Sign-ins to Enterprise Applications and OAuth consents
- DNS and proxy/CASB logs
- Corporate card spending
- Corporate AI, Defender and endpoint logs
Meetings and surveys
Demand
What users need and want: something no log can capture. The map of demand.
- Current use and tools
- Perception: what is allowed and what is not
- Tasks they would like to automate
- Framed as enablement, not as an audit
Where we stand
Maturity
An X-ray of how AI is integrated and governed today, dimension by dimension.
- Policy and governance
- Identity, data and security
- Architecture and integration
- Training and people
- Operations and lifecycle
- Value and use case portfolio
Five maturity levels
From shadow AI to strategic AI
Level 1
Scattered
Shadow AI
Individual use with personal accounts, with no policy or visibility.
Level 2
Aware
Reactive
There is a policy and some approved tools, but it is neither followed nor measured.
Level 3
Defined
Structured
Approved catalog, SSO access, basic controls and an AI owner.
Level 4
Managed
Governed and measured
AI integrated with systems via MCP/API, with traceability and cost and quality control. Prioritized and measured portfolio of use cases.
Level 5
Optimized
Strategic
A scalable, continuously improving capability tied to the business. New use cases are industrialized quickly and securely.
What level is your organization at? The assessment tells you, dimension by dimension.
From assessment to action
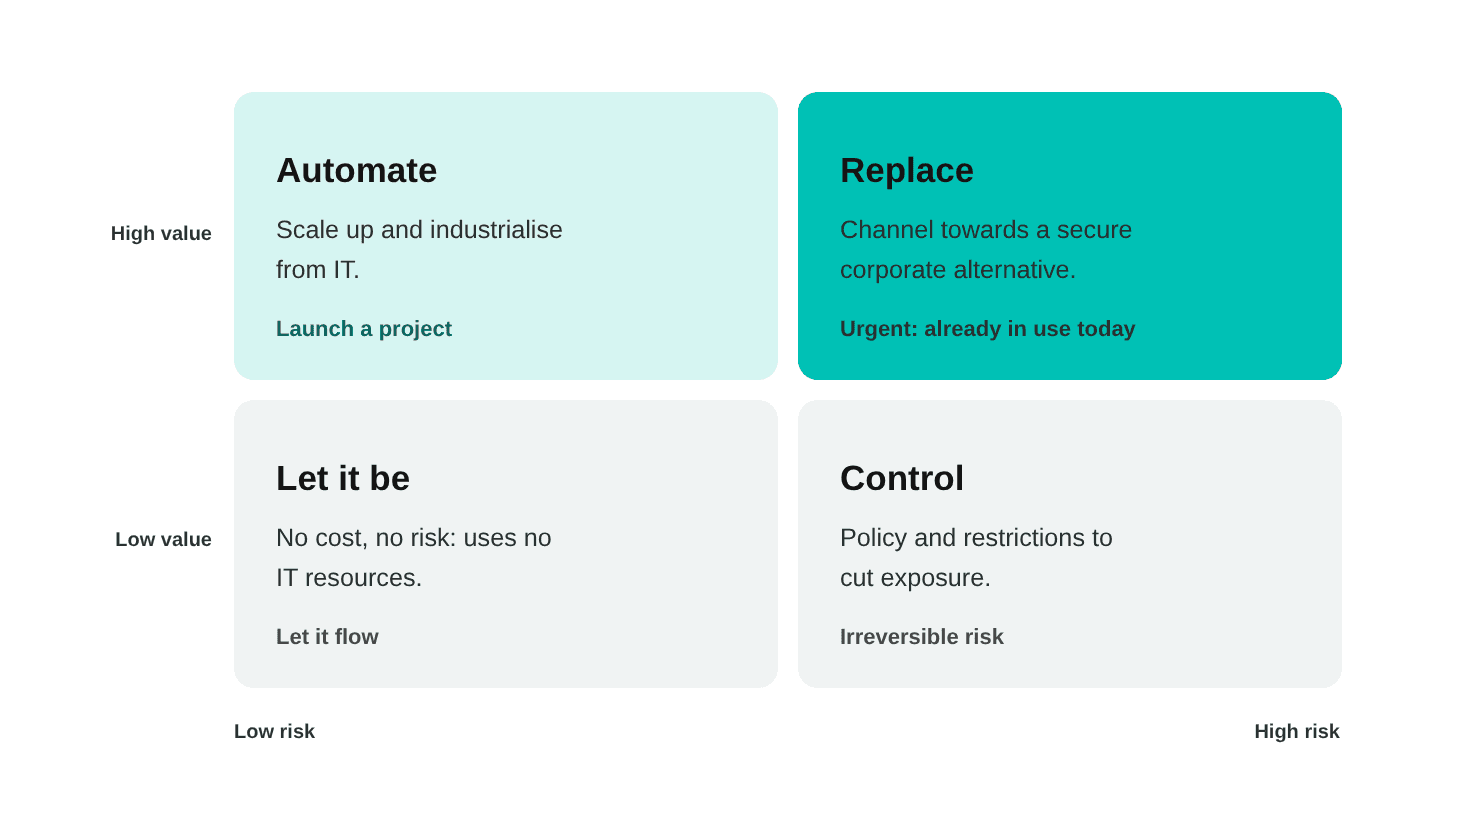
Each use of AI we detect is prioritized according to its risk and value, and receives a specific action.
The high-value uses we detect can go straight into production with our AI Automation and Agents service.
How we work
01
Scoping
What is analyzed, with which sources and with whom.
02
Analysis
Telemetry, meetings or surveys and maturity level.
03
Results
Assessment report and prioritized action plan, presented to your team.
04
Follow-up (optional)
Repeat the assessment every 3–6 months to measure progress.
What you get
Concrete deliverables, ready for decision-making and to share across the organization.
Map of real AI use
Corporate and shadow AI, by area and tool.
Maturity level by dimension
Scale 1–5 and the path to the next level.
Risk × value matrix
Each initiative classified as control, replace, automate or leave as is.
Prioritized action plan
Quick wins and long-term initiatives, ready to decide on.
Usage policy and approved catalog
A proposal ready to communicate to the organization.
A measurable starting point
Repeatable every 3–6 months to measure progress.
All of this, in a single assessment. We start by scoping what is analyzed, with which sources and with whom.
Why Itequia?
AI at the core of how we work. Our own AI-Driven method, applied across the entire lifecycle, to take solutions to production in weeks, not months.
We build it, we run it. Consulting, development, Microsoft and cybersecurity with a single partner, from assessment to operations, with the same point of contact throughout.
Security we practice. ISO 27001 certified, with automated code security analysis in every delivery and experience in regulated environments: banking, pharma, manufacturing and the public sector.
Your feedback, with its own channel. A Customer Experience team, independent from the people delivering your project, tracks your satisfaction so we can correct course in time.


Organizations that trust us
Frequently asked questions
It is the use of AI tools not approved or controlled by IT, often with personal accounts. The risk lies in sensitive data, regulatory compliance and legal exposure. In addition, IT cannot see or measure that use.
No. It is independent of whether you use Copilot, Claude, Gemini or other tools. We analyze the real use of AI, whether corporate or not.
From three sources: telemetry (sign-ins, OAuth consents, DNS and proxy logs, corporate card spending, Defender and endpoint), meetings or surveys with users, and a maturity evaluation across six dimensions.
No. We frame it as enablement: we want to understand what users need and which tasks they would like to automate. If you prefer, surveys can be anonymous with Opinatics.
A map of real AI use, your maturity level by dimension, the risk × value matrix, a prioritized action plan and a proposed usage policy with a catalog of approved tools.
With Tokenmaxxing, each area creates its own agents. It is fast, but hard to govern and token spending grows out of control. With an AI-Factory, IT industrializes automation with approved agents that work via MCP on governed software.
We recommend repeating it every 3–6 months to measure progress. The initiatives that come out of the "Automate" quadrant can become a project with us.
Do you want to know how AI is really being used in your organization?
Tell us about your situation and we will explain how to get started with an assessment and an action plan. No obligation.